From fragmentedcompliance to financialcrime intelligence.
SecuroQ unifies customer, risk, transaction and investigation signals into one explainable intelligence layer — designed as decision support for compliance teams, with human oversight at every step.
Fragmented systems create noise. Intelligence creates clarity.
Most compliance stacks grew tool by tool. SecuroQ connects those signals into one governed intelligence layer, so teams act on context — not fragments.
Isolated legacy systems
KYC, screening and monitoring data locked in disconnected silos.
Alert fatigue
Analysts drowning in repetitive, low-context alerts.
Manual bottlenecks
Investigations rebuilt by hand for every case and audit.
Unified entity view
Customer, risk and transaction signals resolved to one contextual picture.
Prioritised, explainable alerts
Every alert carries reasoning your analysts and auditors can follow.
Investigation-ready output
Case context assembled automatically — reviewed and decided by humans.
Four engines. One governed intelligence layer.
Each engine strengthens the others — customer context sharpens risk scores, risk informs monitoring, and investigations feed learning back into the layer.
Customer Engine
Dynamic KYC/CDD entity resolution and multi-jurisdiction identity context.
Risk Engine
Continuous behavioural risk scoring with contextual risk tiering.
Transaction Engine
Real-time transaction monitoring with adaptive anomaly detection.
Investigation Engine
Case assembly, link analysis and regulator-ready reporting support for MLRO teams.
AI Governance Trust Layer
Every engine operates under human oversight with explainable models and immutable audit trails. AI proposes; your team decides.
See where your framework stands — before the regulator asks.
Preview how a SecuroQ Health Check benchmarks compliance maturity and AI readiness across your institution.
Illustrative demonstration only — synthetic data, not a formal compliance assessment.
Select an institution type and run the simulated scan.
A partnership that compounds — not a big-bang migration.
Technology-enabled intelligence and advisory, clearly distinct from headcount-only outsourcing.
Land
Low-disruption parallel start alongside your existing stack.
Prove
Shadow analysis, maturity mapping, and validated proof of value.
Expand
Scale across engines and business lines as confidence builds.
Retain
Continuous model recalibration, advisory support, and audit readiness.
Start with one capability. Grow into the platform.
Each module stands alone or connects into the wider intelligence layer.
KYC / CDD
Identity resolution, onboarding risk context and refresh workflows.
AML & CTF
Anti-money-laundering and counter-terrorist-financing capability design.
Transaction Monitoring
Behavioural detection tuned to your risk appetite and typologies.
Sanctions & PEP Screening
Screening coverage with contextual match review support.
AI / RegTech Enablement
Explainable models, governance frameworks and model risk controls.
MLRO Advisory
Advisory support for MLROs — audit preparation to framework design.
Platform Vision
A unified intelligence layer that grows with your institution.
Stay ahead of shifting typologies and regulator expectations.
Curated intelligence briefs, regulatory horizon scanning, MLRO playbooks, and executive webinars.
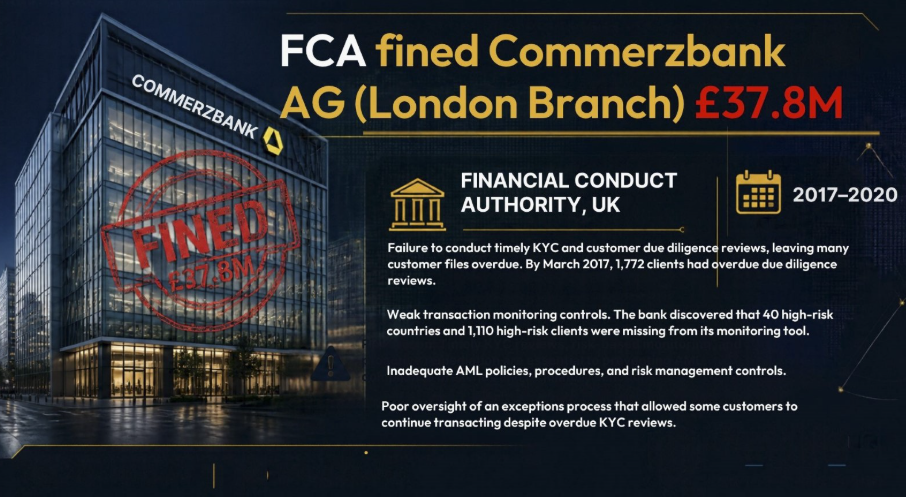
Commerzbank London's £37.8m AML Fine: Turning Historic Gaps into Continuous Controls
The FCA fined Commerzbank London £37,805,400 in June 2020 for weak anti-money laundering (AML) controls between October 2012 and September 2017. Every failing was a gap where continuous, data-driven monitoring is built to close.
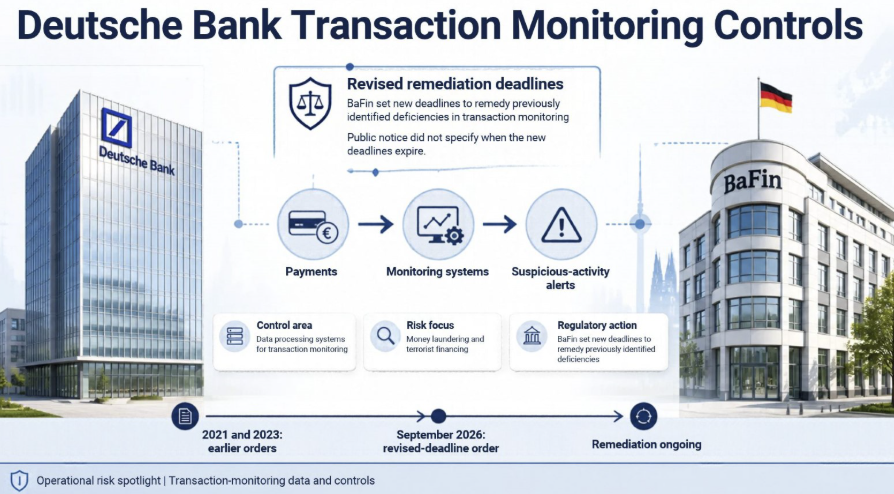
Deutsche Bank and BaFin: Why Transaction Monitoring Cannot Stand Still
Germany’s financial regulator, BaFin, has set Deutsche Bank new deadlines to fix shortcomings in the data-processing systems it uses to monitor transactions for money laundering and terrorist financing. Following earlier remediation orders in 2021 and 2023, the case demonstrates that transaction monitoring cannot be treated as a static one-off project. It must adapt continuously through explainable AI, behavioural risk scoring, and real-time data tuning.
61,800 Bitcoin, Two Courts and One Big Compliance Lesson
Between 2014 and 2017, Qian Zhimin defrauded over 102,000 investors of 40.38B yuan before fleeing China with a laptop holding her bitcoin wallet. On 12 October 2026, the London High Court ruled Chinese law governs victim claims, while a Tianjin court initiated parallel forfeiture. This historic $5.1B crypto asset recovery reveals critical AML lessons in fiat-to-crypto conversion, cross-border jurisdiction, and preventative monitoring.
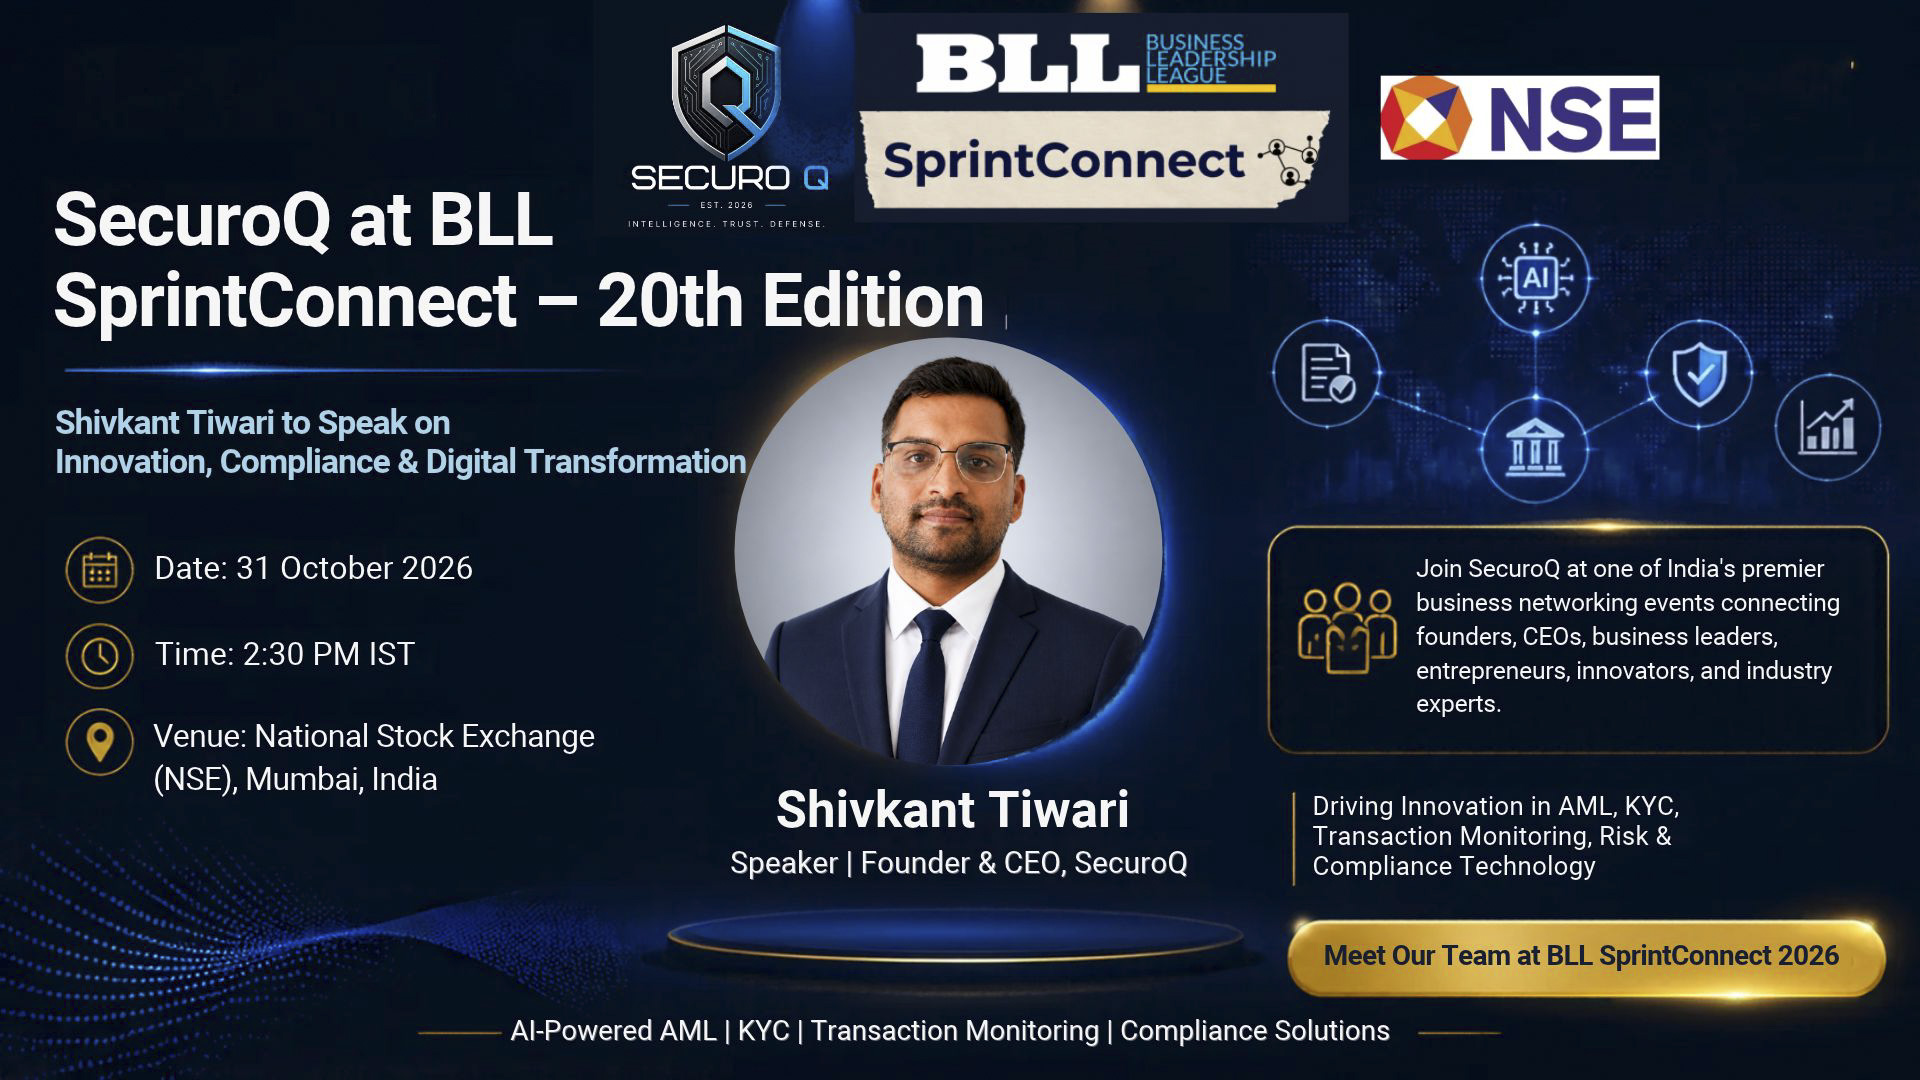
SecuroQ at BLL SprintConnect – 20th Edition
Keynote address by Shivkant Tiwari (Speaker | Founder & CEO, SecuroQ) on Innovation, Compliance & Digital Transformation at the National Stock Exchange (NSE), Mumbai.
Subscribe to SecuroQ FinCrime Intelligence
Receive bi-weekly regulatory horizon scanning, emerging laundering typology alerts, and practical AI governance frameworks directly in your inbox.
Intelligence you can defend — to your board and your regulator.
SecuroQ presents AI as decision support with human oversight, never autonomous compliance judgement.
Human Oversight
AI supports decisions; accountable humans make them. Escalation paths are explicit by design.
Explainability
Model outputs carry reasoning that analysts, MLROs and auditors can interrogate.
Auditability
Decisions, overrides and model changes are designed to be traceable end-to-end.
Security
Security-first architecture with encryption and access controls as core considerations.
Regulatory Adaptability
Configurable to evolving expectations across jurisdictions — without hard-coding one regime.
Compliance is not a checkbox. It is an institutional standard.
Global supervisors no longer judge institutions solely by their written policy documents. Regulators evaluate organizational culture — how decisions are challenged, evidence is documented, and risk is owned across the Three Lines of Defence.
Single source of truth shared across front line, MLRO & audit.
Every alert disposition recorded with explainable reasoning.
Empowering frontline staff to flag anomalies without friction.
AI proposes signals; accountable humans execute judgements.
Executive & Board Accountability
Boards and senior leaders hold personal accountability for compliance culture under SMCR and global standards.
Three Lines of Defence (3LoD)
Connecting onboarding detection (Line 1), MLRO calibration (Line 2), and audit assurance (Line 3).
Evidence Over Tick-Box Bureaucracy
Every risk score, override, and alert disposition carries contemporaneous evidence that stands up to audits.
Psychological Safety & Early Escalation
Incentivizing frontline teams to surface red flags and near-misses without fear of commercial friction.
Tick-Box Compliance vs. Governed Regulatory Culture
How modern tier-1 institutions transform from vulnerable, reactive processes into defensible, audit-ready operational resilience.
Architects of next-generation compliance intelligence.
Led by technologists and compliance innovators dedicated to solving enterprise financial crime.
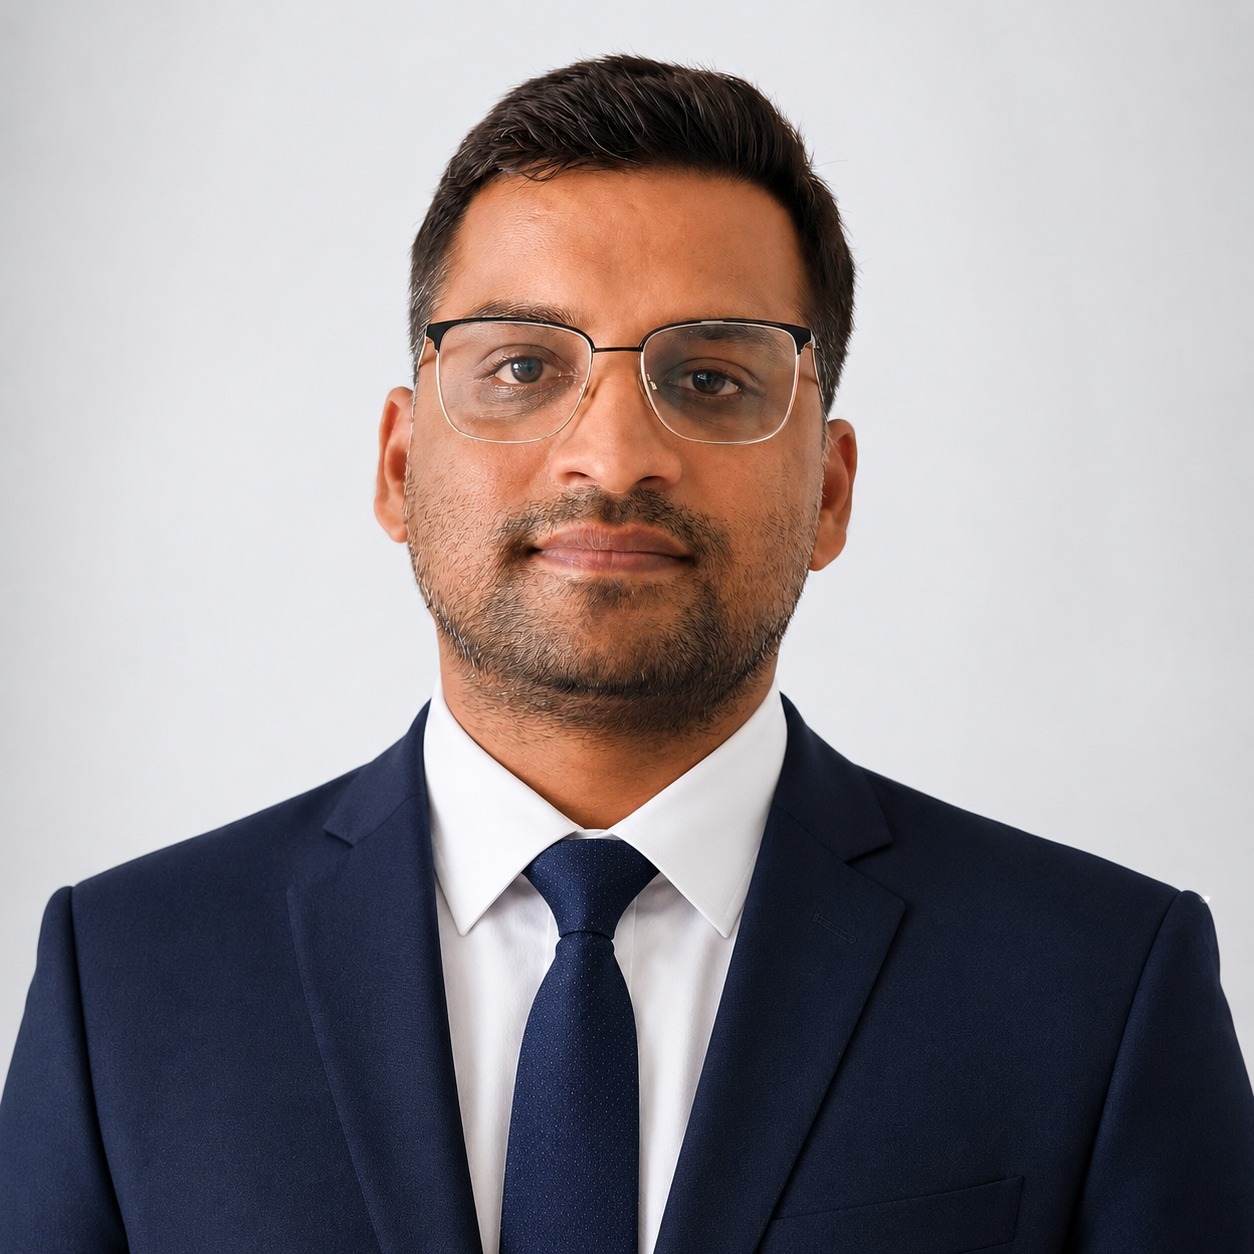
Shivkant Tiwari
FounderSteering SecuroQ's strategic vision to transform fragmented AML compliance into an explainable, enterprise-grade intelligence layer.
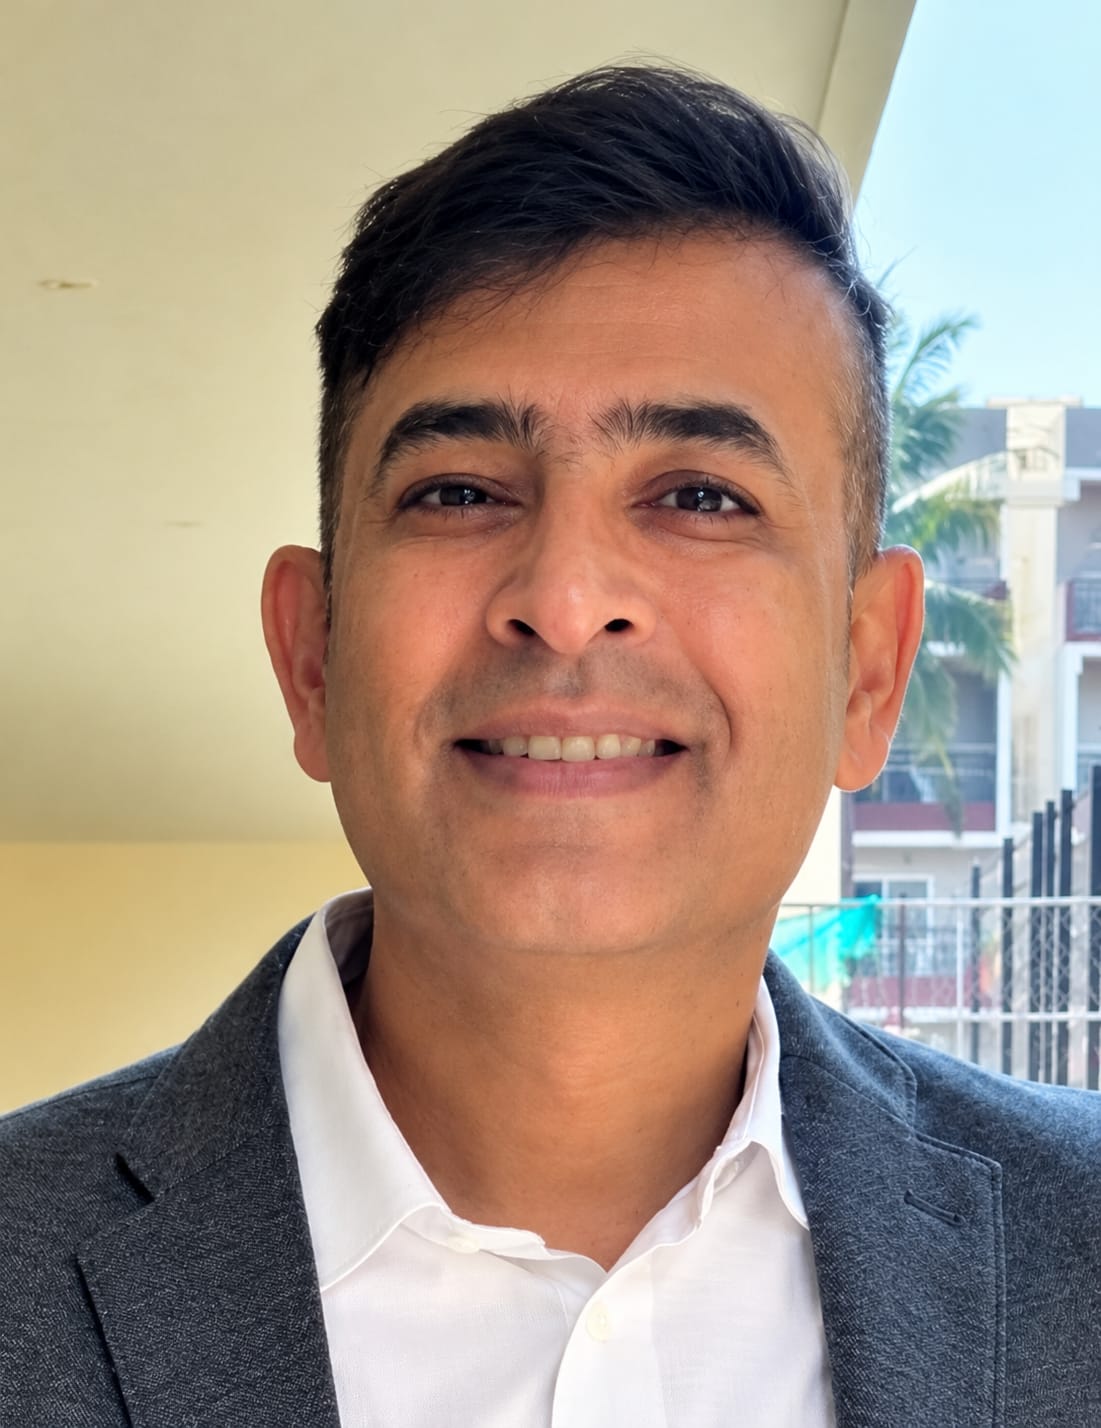
Pratik Badkul
Chief Technology OfficerDirecting engineering and telemetry architecture to deliver high-throughput, low-latency financial crime detection engines.
Book your Financial Crime Health Check.
A structured, confidential review of your financial crime framework — maturity mapping, AI readiness and a prioritised roadmap. Prefer to see the platform first? Request a demo instead.
- Confidential — no obligation
- Delivered by financial crime specialists
- Roadmap you keep, whatever you decide