Commerzbank London's £37.8m AML Fine: Turning Historic Gaps into Continuous Controls
The FCA fined Commerzbank London £37,805,400 in June 2020 for weak anti-money laundering (AML) controls between October 2012 and September 2017. Every failing was a gap where continuous, data-driven monitoring is built to close.
"Every failing identified by the regulator was a gap where continuous, data-driven monitoring is built to close."
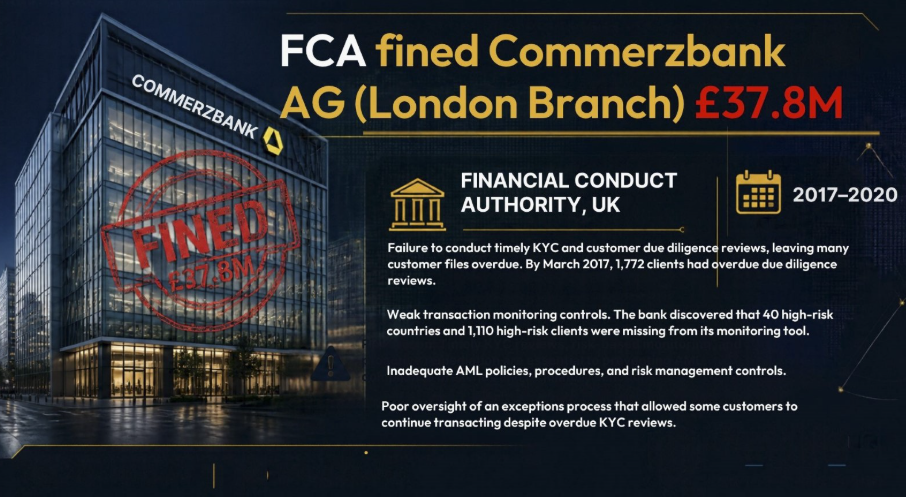
The Financial Conduct Authority (FCA) fined Commerzbank London £37,805,400 in June 2020 for weak anti-money laundering (AML) controls between October 2012 and September 2017. Every failing was a gap where continuous, data-driven monitoring is built to close.
The FCA had warned the bank in 2012, 2015 and 2017, yet the weaknesses stayed. Three major failings stand out:
Three Standout Control Failings
- Weak transaction monitoring: In 2015 the bank found that 40 high-risk countries and 1,110 high-risk clients were missing its monitoring tool, so their activity was not being checked properly.
- Inadequate policies, procedures, and risk controls: The bank did not keep adequate customer due diligence procedures, which breached FCA Principle 3 on risk management systems.
- Poor oversight of exceptions: By 1 March 2017, 1,772 clients were overdue for due diligence reviews, and some kept transacting through an exceptions process that nobody controlled properly.
SecuroQ's AI-led RegTech approach turns each failing into a control that runs all the time, not once a year.
SecuroQ AI Control Remedy & Outcomes
| Failing | SecuroQ AI Remedy | Result |
|---|---|---|
| Missing high-risk countries and clients in the monitoring tool | Automated coverage checks that match every customer, account and high-risk country against the monitoring scope, and flag any gap straight away | No client or country goes unmonitored |
| Inadequate policies, procedures and risk controls | Risk-based customer scoring and rule tuning that keep controls in line with current risk, with explainable alerts and a full audit trail | Controls that can be shown to the regulator |
| Overdue KYC reviews and an uncontrolled exceptions process | Risk-triggered KYC refresh, automatic escalation of overdue reviews, and alerts on activity by overdue accounts. Every exception is logged, time-limited and reported to senior management | Exceptions stay rare, visible and closed on time |
From Annual Compliance Checkboxes to 24/7 Autonomous Assurance
When monitoring and KYC reviews depend on annual cycles, blindspots inevitably widen. SecuroQ replaces periodic sampling with real-time automated coverage verification, dynamic risk scoring, and zero-leakage exception governance.
Disclaimer: This article is for general industry awareness and educational purposes, based on publicly reported regulatory notices. It demonstrates RegTech application principles and does not imply any wrongdoing beyond the facts published by regulators.
Eliminate Transaction Monitoring Blindspots with Continuous AI Controls
Discover how SecuroQ's automated coverage reconciliation, dynamic KYC refresh, and real-time exception governance protect regulated institutions from supervisory enforcement.